FPR1010-NGFW-K9 – 8x1G RJ45 Ports (2 PoE+) – 60W PoE Budget – NGFW Firewall

Why Layer23-Switch
Stocked, Shipped and Supported by One Team
Ships in 1 Business Day
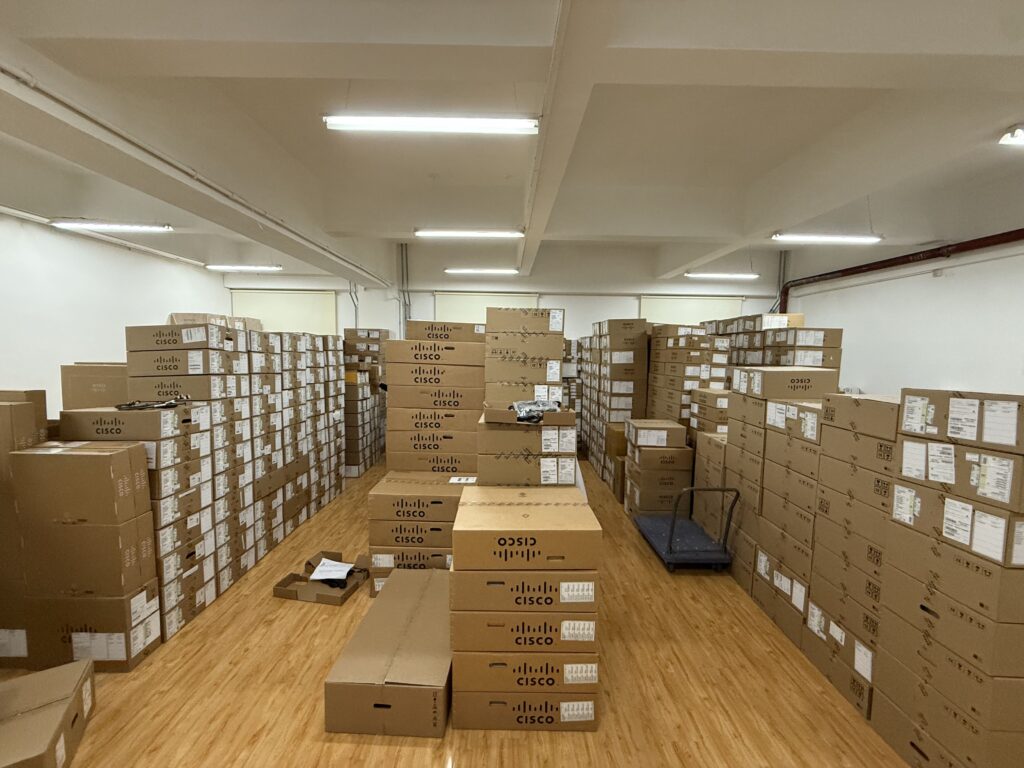
In-stock orders leave our Hong Kong or U.S. warehouse within 1 business day after payment, with tracking by email.
LSCare Warranty
3years on enterprise equipment
Free CCIE Support
Certified engineers help before and after you buy. Reply within 1 business day by email or live chat.
Verify Before You Pay
100%factory-sealed
Get label and serial photos before shipment, and check every serial number with Cisco.
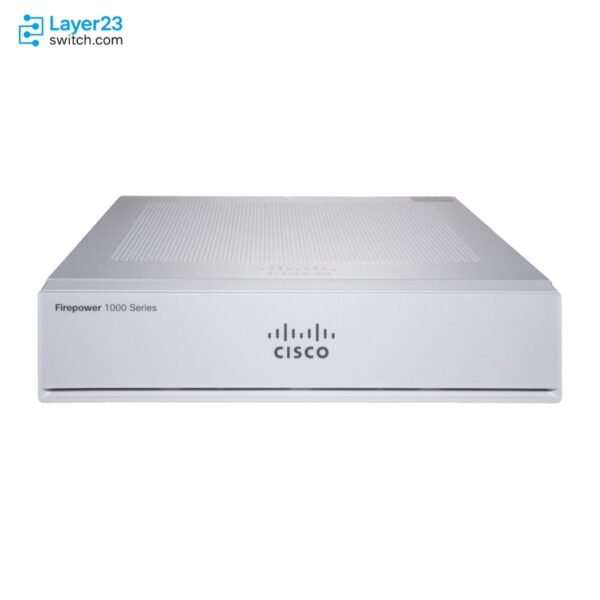
FPR1010-NGFW-K9 Description
The FPR1010-NGFW-K9 is a Cisco Firepower 1010 next-generation desktop firewall running Threat Defense software at the internet edge of a small office or remote branch. The appliance is rated at 880 Mbps of firewall, AVC and IPS throughput with 1024-byte packets, has eight 1G RJ-45 ports with PoE+ on two of them from a 60W budget, and supports 75 VPN peers. IPS, malware defense and URL filtering are enabled by Threat Defense subscriptions, and those subscriptions cannot be added to a Firepower 1010 that runs ASA software.
Quick Specs
|
Parameter |
Specification |
|---|---|
|
Software application |
Cisco Secure Firewall Threat Defense |
|
Network ports |
8 x 10/100/1000 RJ-45 (Ethernet 1/1 to 1/8) |
|
PoE+ ports |
Ethernet 1/7 and 1/8, IEEE 802.3at, up to 30W per port |
|
Default PoE budget |
60W PoE+ power |
|
Default power supply |
PWR-DT-150W-AC, 150W AC, external |
|
Throughput: FW + AVC (1024B) |
890 Mbps |
|
Throughput: FW + AVC + IPS (1024B) |
880 Mbps |
|
IPSec VPN throughput |
400 Mbps (1024B TCP with Fastpath) |
|
Maximum concurrent sessions, with AVC |
100K |
|
Maximum VPN peers |
75 |
|
High availability |
Active/Standby |
|
Form factor |
Compact desktop, fanless, 0 dBA |
|
Minimum Threat Defense release for switch ports and PoE+ |
6.5 |
Product Performance
Key Features
With application visibility and IPS both enabled, the appliance is rated at 880 Mbps using 1024-byte packets, against 890 Mbps for firewall and AVC alone. TLS throughput is rated separately at 195 Mbps, and every figure moves with the features enabled, the protocol mix and the packet size.
Application visibility across more than 4,000 applications and Security Intelligence on IP, URL and DNS reputation are standard. IPS, Malware Defense and URL filtering across more than 80 categories become active with the Threat, Malware and URL subscriptions, and Malware or URL filtering requires the Threat subscription alongside it.
Ethernet 1/7 and 1/8 power endpoints at up to 30W each under IEEE 802.3at, drawing on 60W of PoE+ power from the 150W supply. Power is negotiated over LLDP, and PoE+ on these ports needs Threat Defense 6.5 or later with the ports set as switch ports.
Each network port runs as a firewall interface or as a Layer 2 hardware switch port, with Ethernet 1/1 as the firewall interface and Ethernet 1/2 to 1/8 in VLAN 1 by default. Hosts on the same VLAN are switched in hardware without passing the Threat Defense policy, and VLAN interfaces do not run dynamic routing, multicast routing or ECMP.
High availability runs only as an Active/Standby pair; clustering and multiple context mode are not supported. Switch ports keep forwarding on both units and create a loop, so a pair uses an external switch for the LAN and a firewall interface for the failover link.
Cisco Device Manager configures a single unit on site. A multi-site deployment manages the appliance from a Firewall Management Center, or from the cloud through Cisco Defense Orchestrator, for centralized policy, logging and reporting.
Application Scenarios
In a small office, the appliance terminates the internet circuit on Ethernet 1/1 and applies IPS and URL filtering to user traffic, while desktops and printers plug into its built-in switch ports.
A company with many small branches places one unit at each site as the site-to-site VPN endpoint and pushes a common policy to all of them from a Firewall Management Center or Cisco Defense Orchestrator.
A clinic or retail store without a wiring closet can keep the fanless 0 dBA unit in an occupied back office. There it powers an access point or IP phone from a PoE+ port and protects the front-desk or point-of-sale network.
Product Comparison
|
Parameter |
FPR1010-NGFW-K9 |
FPR1010E-NGFW-K9 | ||
|---|---|---|---|---|
|
Throughput: FW + AVC (1024B) |
890 Mbps |
Not applicable |
890 Mbps |
2.3 Gbps |
|
Stateful inspection firewall throughput |
Not applicable |
2 Gbps (1500B UDP) |
Not applicable |
Not applicable |
|
Throughput: FW + AVC + IPS (1024B) |
880 Mbps |
Not applicable |
880 Mbps |
2.3 Gbps |
|
IPsec VPN throughput |
400 Mbps (1024B TCP with Fastpath) |
500 Mbps (450B UDP L2L test) |
400 Mbps (1024B TCP with Fastpath) |
1.2 Gbps (1024B TCP with Fastpath) |
|
Maximum concurrent sessions, with AVC |
100K |
Not applicable |
100K |
200K |
|
Maximum VPN peers |
75 |
75 |
75 |
150 |
|
Network interfaces |
8 x 1000BASE-T |
8 x 1000BASE-T |
8 x 1000BASE-T |
8 x 1000BASE-T, 4 x SFP |
|
Power over Ethernet |
2 ports PoE+ (IEEE 802.3at), 60W default PoE budget |
2 ports PoE+ (IEEE 802.3at), 60W default PoE budget |
Not supported |
Not supported |
|
Power supply configuration |
External AC, PWR-DT-150W-AC 150W |
External AC, PWR-DT-150W-AC 150W |
External AC, PWR-DT-66WAC 66W |
Integrated, single AC input |
FPR1010-NGFW-K9 and FPR1010E-NGFW-K9 share the 880 Mbps Threat Defense rating with IPS, but only FPR1010-NGFW-K9 powers Ethernet 1/7 and 1/8 with PoE+ from a 60W budget. FPR1010E-NGFW-K9 has no PoE and a 66W supply, which suits sites where every access point and phone has its own power. More than 880 Mbps with IPS, more than 75 VPN peers or SFP fiber ports move the site to FPR1120-NGFW-K9, a 1RU model with 2.3 Gbps, 150 peers and four SFP ports but no PoE. FPR1010-ASA-K9 is the same PoE+ hardware ordered with ASA software at 2 Gbps of stateful inspection. It suits sites that need only stateful firewalling and VPN, since Threat, Malware and URL subscriptions attach only to the Threat Defense chassis.
PoE Power Planning
|
Planning Item |
Value or Check |
|---|---|
|
PoE-capable ports |
Ethernet 1/7 and 1/8 only; Ethernet 1/1 to 1/6 carry no power |
|
PoE standards and per-port limit |
IEEE 802.3af PoE and 802.3at PoE+, up to 30W per port |
|
Total PoE budget |
60W of PoE+ power on the default PWR-DT-150W-AC supply |
|
Device count |
Two powered endpoints at most, one per PoE+ port; two 30W endpoints use the full 60W |
|
Power negotiation |
PoE is enabled by default; PoE+ power is negotiated over LLDP and supplied only as needed |
|
Conditions that remove power |
Shutting the interface down stops power; EtherChannel member ports do not support PoE |
|
Software baseline |
Threat Defense 6.5 or later, with Ethernet 1/7 and 1/8 configured as switch ports |
Ordering Checklist
- Threat Defense subscription: The configurator adds a 3-year Threat, Malware and URL subscription by default; change it to another combination such as L-FPR1010T-T-3Y or L-FPR1010T-TC-5Y in a 1-, 3- or 5-year term. Malware and URL features do not work without the Threat subscription.
- Smart Account: Assign a Cisco Smart Licensing account before the order is placed, because the licenses and subscriptions are deposited there. Only the 3-month evaluation license activates without one.
- Failover pair: Order FPR1010-FTD-HA-BUN for two identical chassis with subscriptions, or a second FPR1010-NGFW-K9 with its own subscription. An active-passive Threat Defense pair needs two subscriptions.
- Remote access VPN: Add Cisco Secure Client licenses when remote users will connect. Remote Access VPN on Threat Defense does not run without them.
- Mounting kit: Order FPR1010-RACK-MNT= for a 2 RU rack shelf sized for the 150-W supply, or FPR1K-DT-WALL-MNT= for wall mounting. The 150-W supply does not fit the original shelf, and FPR1K-DT-RACK-MNT= is the shelf for the 66-W supply.
- Power cord: Select the country C13 power cord with the order, or supply an approved cord. The cord is a separate order option, and only approved cords are supported.
Optional Add-ons
|
Model |
Description |
|---|---|
|
L-FPR1010T-TMC= |
Threat Defense Threat, Malware and URL license for Firepower 1010 |
|
L-FPR1010T-T= |
Threat Defense Threat Protection license for Firepower 1010 |
|
PWR-DT-150W-AC= |
Spare 150W desktop AC power supply for Firepower 1010 |
|
FPR1010-RACK-MNT= |
Rack-mount kit for Firepower 1010 with the 150W AC power supply |
|
FPR1K-DT-WALL-MNT= |
Wall-mount kit for Firepower 1010 and 1010E |
|
FPR1K-DT-FIPS-KIT= |
FIPS kit for Firepower 1010 |
|
FPR1K-DT-ACY-KIT= |
Accessory kit for Firepower 1010 |
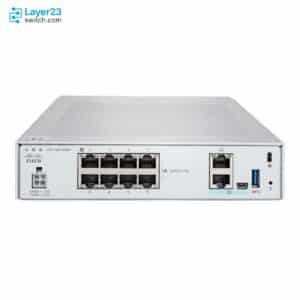
FPR1010-NGFW-K9 Front View
|
1 |
Status LEDs |
2 |
Management port |
|
3 |
Lock slot |
4 |
Power cord socket |
|
5 |
Network data ports |
6 |
Console port |
|
7 |
USB Mini B port |
8 |
USB Type A port |
|
9 |
Reset button |
10 |
Rubber feet |
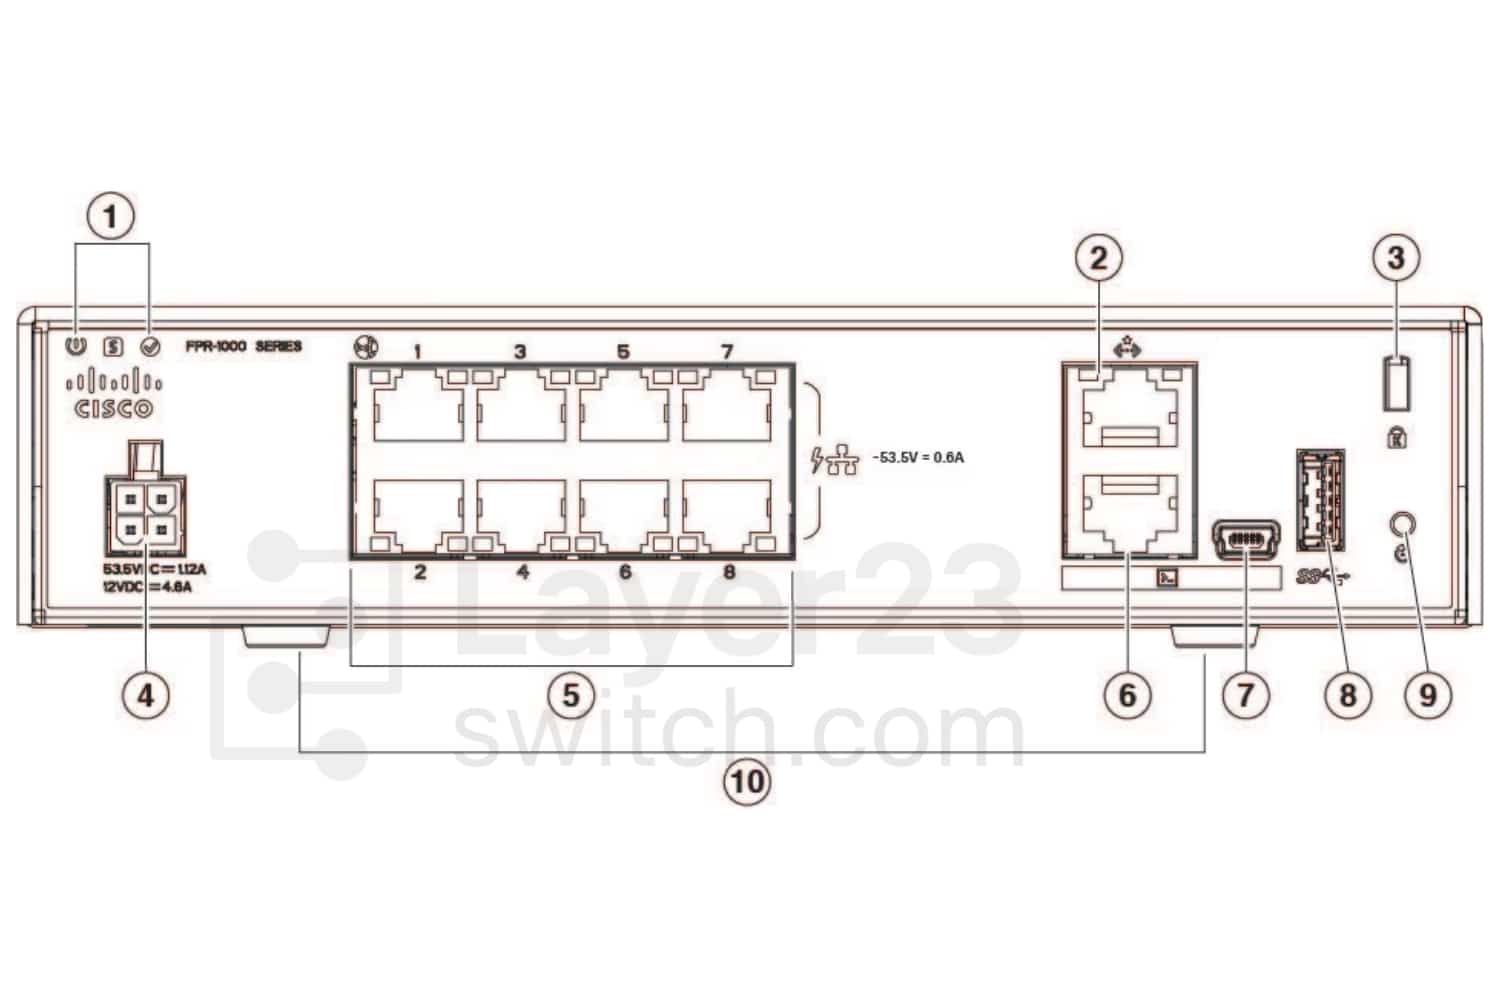
Specifications
| Parameter | Specification | Parameter | Specification |
|---|---|---|---|
| Product ID | FPR1010-NGFW-K9 | Software application | Cisco Secure Firewall Threat Defense with optional subscriptions; the hardware also supports Cisco Secure Firewall ASA |
| Network interfaces | 8 x 1000BASE-T, RJ-45 10/100/1000 (Ethernet 1/1 to 1/8), auto MDI/X | Interface modes | Each network port configurable as a firewall interface or Layer 2 hardware switch port (access or 802.1Q trunk); by default Ethernet 1/1 is a firewall interface and Ethernet 1/2 to 1/8 are switch ports in VLAN 1 |
| Power over Ethernet | 2 ports PoE+ (IEEE 802.3at) on Ethernet 1/7 and 1/8, IEEE 802.3af also supported, up to 30W per port | Default PoE budget | 60W PoE+ power |
| Management interfaces | 1 x 1000BASE-T management port; 1 x RJ-45 serial console; 1 x USB Mini B console | USB | 1 x USB 3.0 Type-A for external storage |
| Throughput: FW + AVC (1024B) | 890 Mbps | Throughput: FW + AVC + IPS (1024B) | 880 Mbps |
| Throughput: NGIPS (1024B) | 900 Mbps | Transport Layer security (TLS) | 195 Mbps |
| IPSec VPN throughput | 400 Mbps (1024B TCP with Fastpath) | Maximum VPN peers | 75 |
| Maximum concurrent sessions, with AVC | 100K | Maximum new connections per second, with AVC | 6K |
| AVC | Standard, more than 4,000 applications plus geolocations, users and websites; OpenAppID custom detectors | Cisco security intelligence | Standard, with IP, URL and DNS threat intelligence |
| Cisco IPS | Available with the Threat subscription | Cisco malware Defense for networks | Available with the Malware subscription; Cisco Malware Analytics sandboxing available |
| URL filtering | More than 80 categories and more than 280 million categorized URLs, with the URL subscription | High availability | Active/Standby |
| Clustering | Not supported | Multiple context mode | Not supported |
| Named interfaces, maximum | 60 | DRAM | 8 GB |
| SSD storage | 1 x 200 GB M.2 SATA SSD, not field-replaceable | Default power supply | PWR-DT-150W-AC, external 150W AC (150 W of +12 VDC system power) |
| System power | 30 W, not including connected PoE devices | AC maximum power draw | 115W |
| AC input voltage | 100 to 240V AC | AC input frequency | 50 to 60 Hz |
| AC maximum current draw | < 2A at 100V, < 1A at 240V | AC efficiency | >88% at 50% load |
| Power switch | No power switch; the chassis powers on when the AC power supply is plugged in | Fan modules | No fan; side-to-side airflow |
| Noise | 0 dBA | Form factor | Compact desktop or wall mount; 2 RU with the rack-mount shelf |
| Dimensions (H x W x D) | 1.82 x 7.85 x 8.07 in. (4.62 x 19.94 x 20.50 cm) | Rack-mount shelf dimensions (H x W x D) | 3.06 x 17.40 x 21.65 in. (7.77 x 44.2 x 54.99 cm) for the 150W supply |
| Weight | 1.36 kg (3 lb) | Temperature: operating | 0°C to 40°C (32°F to 104°F); maximum derated 1.5°C per 1000 ft of altitude |
| Temperature: nonoperating | -25°C to 70°C (-13°F to 158°F) | Humidity: operating | 90% noncondensing |
| Humidity: nonoperating | 10 to 90% noncondensing | Altitude: operating | 9,843 ft (3,000 m) |
| Altitude: nonoperating | 15,000 ft (4,570 m) | Physical security | Kensington T-bar lock slot |
| Reset button | Held for more than three seconds, it restores the default configuration after the next reboot | Minimum Threat Defense release | 6.5 for switch ports and PoE+ |
| Threat Defense compatibility | Management Center and Device Manager: 6.4, 6.6, 6.7, 7.0 to 7.3, 7.4.1 and later 7.4.x, 7.6, 7.7 and 10.x; 7.4.0 not supported | Management | Cisco Device Manager for local management; Firewall Management Center or Cisco Defense Orchestrator for centralized management |
| Regulatory compliance | CE markings per directives 2004/108/EC and 2006/108/EC | Safety certifications | UL 60950-1, CAN/CSA-C22.2 No. 60950-1, EN 60950-1, IEC 60950-1, AS/NZS 60950-1, GB4943 |
| EMC: emissions | 47CFR Part 15 Class A (FCC Class A), AS/NZS CISPR22 Class A, CISPR22 Class A, EN55022 Class A, ICES003 Class A, VCCI Class A, EN61000-3-2, EN61000-3-3, KN22 Class A, CNS13438 Class A, EN300386, TCVN7189 | EMC: immunity | EN55024, CISPR24, EN300386, KN24, TVCN 7317, EN-61000-4-2, EN-61000-4-3, EN-61000-4-4, EN-61000-4-5, EN-61000-4-6, EN-61000-4-8, EN61000-4-11 |
| Supply chain assurance | Cisco Trust Anchor Technologies | Package contents | Chassis and power supply; USB console cable (37-1977-01) and country-specific power cord when ordered |
Quality Certifications
Customer Reviews
Questions & Answers
-
What throughput does FPR1010-NGFW-K9 provide with IPS enabled?
-
Do IPS and URL filtering on FPR1010-NGFW-K9 need a subscription?
-
Can FPR1010-NGFW-K9 be ordered with a Small Business Edition subscription?
-
Which subscription PIDs add Threat plus Malware, or Threat plus URL, to FPR1010-NGFW-K9?
-
Does FPR1010-FTD-HA-BUN discount the second Threat Defense subscription for FPR1010-NGFW-K9?
-
Can FPR1010-NGFW-K9 run Threat Defense 7.4.0?
-
Which power cord PIDs fit FPR1010-NGFW-K9?
-
Can both console ports on FPR1010-NGFW-K9 be used at the same time?
-
What is the maximum power draw of FPR1010-NGFW-K9?
Warranty
Layer23-Switch.com offers genuine, high-quality ICT products at competitive wholesale prices—ensuring exceptional value without compromising quality.
All items are brand new, original, and factory-sealed.
Upon request, each unit can be fully tested and verified by a Cisco CCIE-certified engineer to ensure perfect working condition before shipment.
Our Cisco CCIE-certified experts provide free professional support via phone, email, online chat, or remote login—helping you deploy and troubleshoot with confidence.
If you are not satisfied with your purchase, you may request an exchange or full refund. Our customer service team will guide you through the return process quickly and smoothly. Visit Return Policy page for more information.
We support multiple secure payment and logistics options, backed by industry-leading verification:
Visit How to Pay page for more information
Extended, Worry-Free Warranty Coverage Factory New Sealed Enterprise Hardware:
· 3 Years Factory New Sealed
Visit Warranty Policy page for more information
Verify, plan, and comparewith confidence
Use practical tools to check device details, review lifecyclemilestones, and compare hardware before you buy.
Stretched our IT budget further than we thought possible.
Our purchasing agent said the quoting process was the smoothest she’s experienced.
Met all our expectations. Solid choice.
Box was brand new and sealed. Invoice was correct.
Shipped to UK with no issues. VAT receipt provided promptly.