
FPR2110-NGFW-K9 – 12x1G RJ45 Ports – 4x1G SFP Ports – NGFW Firewall


Why Layer23-Switch
Stocked, Shipped and Supported by One Team
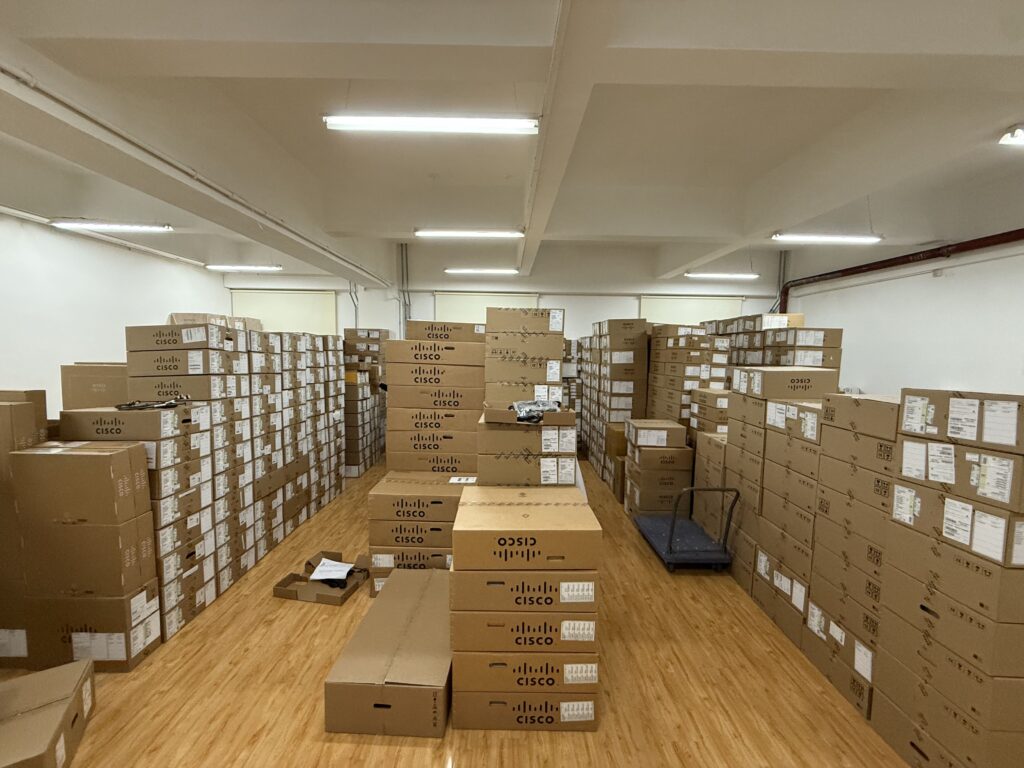
Ships in 1 Business Day
In-stock orders leave our Hong Kong or U.S. warehouse within 1 business day after payment, with tracking by email.
LSCare Warranty
3years on enterprise equipment
Free CCIE Support
Certified engineers help before and after you buy. Reply within 1 business day by email or live chat.
Verify Before You Pay
100%factory-sealed
Get label and serial photos before shipment, and check every serial number with Cisco.
FPR2110-NGFW-K9 Description
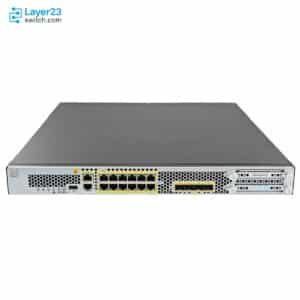
The FPR2110-NGFW-K9 is a Cisco Firepower 2110 next-generation firewall that runs Firepower Threat Defense at the edge of a branch or campus network. With application control and IPS both active, Threat Defense is rated at 2.6 Gbps on 1024-byte packets and holds 1 million concurrent sessions, with 1,500 VPN peers on twelve 1G RJ-45 ports and four 1G SFP ports. The appliance includes the Essentials license only, and IPS, Malware Defense and URL filtering start working once a separate subscription is applied.
Quick Specs
|
Parameter |
Specification |
|---|---|
|
Software application |
Cisco Firepower Threat Defense |
|
Network interfaces |
12 x 10M/100M/1GBASE-T RJ-45 (Ethernet 1/1 to 1/12) |
|
SFP ports |
4 x 1G SFP (Ethernet 1/13 to 1/16) |
|
Network modules |
No network module bay |
|
Throughput: FW + AVC + IPS (1024B) |
2.6 Gbps |
|
Maximum concurrent sessions, with AVC |
1 million |
|
IPSec VPN throughput |
950 Mbps (1024B TCP with Fastpath) |
|
Maximum VPN peers |
1,500 |
|
Included license |
Essentials; IPS, Malware Defense and URL Filtering by subscription |
|
High availability |
Active/Standby |
|
Power supply configuration |
Single integrated 250W AC, no redundancy |
|
Form factor |
1RU, 2-post mount brackets included |
Product Performance
Key Features
Turning on IPS costs no rated throughput on this model: firewall with AVC and firewall with AVC and IPS are both rated at 2.6 Gbps on 1024-byte packets. TLS inspection is rated separately at 365 Mbps, and new sessions open at 14K per second.
Application visibility across more than 4,000 applications and Security Intelligence on IP, URL and DNS reputation are standard. IPS, Malware Defense and URL filtering across more than 80 categories need the Threat, Malware and URL subscription before they inspect any traffic.
The 100 GB system SSD occupies slot 1, and slot 2 stays empty for the Malware Storage Pack, which stores threat detection results for later analysis and supports Malware Defense. The software does not support SSD hot swap, so the chassis is powered down to add or replace a drive.
Threat Defense pairs two appliances only as Active/Standby. One unit carries all traffic while the other waits, which keeps the pair’s inspection capacity at the 2.6 Gbps rating of a single appliance.
Firepower Device Manager configures one appliance on site. Larger estates register it to Management Center or Cisco Defense Orchestrator for central configuration, logging, monitoring and reporting, and Management Center then delivers every license to the appliance.
Twelve 1G RJ-45 ports and four 1G SFP ports are the whole interface layout, with no network module bay. The 250W AC supply and the fans are fixed parts, and a failure of either means an RMA of the chassis.
Application Scenarios
In a branch office, the appliance terminates the internet circuit and inspects user traffic with IPS and URL filtering, at up to 2.6 Gbps on 1024-byte packets.
Retail chains and other multi-site organizations register an appliance at each location to a Management Center, or to Cisco Defense Orchestrator in the cloud, and push one policy with central logging.
Inside a small data room, the firewall stands between user VLANs and a server segment, applying application control and Security Intelligence reputation filtering to east-west traffic.
Product Comparison
|
Parameter |
FPR2110-NGFW-K9 | |||
|---|---|---|---|---|
|
Stateful inspection firewall throughput (1500B UDP) |
Not applicable |
3 Gbps |
Not applicable |
Not applicable |
|
Throughput: FW + AVC + IPS (1024B) |
2.6 Gbps |
Not applicable |
3.4 Gbps |
5.4 Gbps |
|
IPSec VPN throughput |
950 Mbps (1024B TCP with Fastpath) |
500 Mbps (450B UDP L2L test) |
1.2 Gbps (1024B TCP with Fastpath) |
1.9 Gbps (1024B TCP with Fastpath) |
|
Maximum concurrent sessions |
1 million (with AVC) |
1 million |
1.5 million (with AVC) |
2 million (with AVC) |
|
Maximum VPN peers |
1,500 |
1,500 |
3,500 |
7,500 |
|
Integrated I/O |
12 x RJ-45, 4 x 1G SFP |
12 x RJ-45, 4 x 1G SFP |
12 x RJ-45, 4 x 1G SFP |
12 x RJ-45, 4 x 10G SFP+ |
|
Network modules |
No network module bay |
No network module bay |
No network module bay |
1 bay (10G SFP+, 1/10G FTW options) |
|
Power supply configuration |
Single integrated 250W AC |
Single integrated 250W AC |
Single integrated 250W AC |
Single 400W AC; dual 400W AC or 350W DC optional |
|
High availability |
Active/Standby |
Active/Active and Active/Standby |
Active/Standby |
Active/Standby |
FPR2110-NGFW-K9 runs Threat Defense on the same Firepower 2110 hardware that FPR2110-ASA-K9 runs with ASA, and only the Threat Defense model takes the IPS, Malware Defense and URL subscription. A site that needs just stateful firewalling and VPN, or an Active/Active failover pair, can drop to FPR2110-ASA-K9 at 3 Gbps of stateful inspection and give up IPS and URL inspection. Past 2.6 Gbps with IPS, 1 million sessions or 1,500 peers, FPR2120-NGFW-K9 keeps the same sixteen ports at 3.4 Gbps, 1.5 million and 3,500. A design that needs 10G SFP+ links, a network module or dual power supplies moves to FPR2130-NGFW-K9, rated at 5.4 Gbps with IPS.
Ordering Checklist
- Threat, Malware and URL subscription: Add L-FPR2110T-TMC= and pick the L-FPR2110T-TMC-1Y, -3Y or -5Y term. Only Essentials comes with the appliance, so IPS, Malware Defense and URL Filtering stay off without it.
- Smart Account: Link the licenses to the Smart Software Licensing account that the Management Center registers with. The Management Center supplies every license to the appliance from that account.
- Remote access VPN: Add Cisco Secure Client licenses, ordered under the Cisco Secure Client Ordering Guide, when remote users will connect; they are separate from the Essentials license and the TMC subscription.
- Malware Storage Pack: Add FPR-MSP-SSD when malware analysis results need local storage. The MSP installs only in SSD slot 2, which ships empty.
- Rack rails: Two 2-post mount brackets come with the chassis; add FPR2K-SLIDE-RAILS for a 4-post EIA-310-D rack.
- Power cord: Select the country power cord with the system. Orders for Argentina, Brazil or Japan must carry CAB-ACR, CAB-C13-ACB or CAB-JPN on the same order.
Optional Add-ons
|
Model |
Description |
|---|---|
|
L-FPR2110T-TMC= |
IPS, Malware Defense and URL Filtering license for Firepower 2110 Threat Defense |
|
L-FPR2110T-TMC-1Y |
1-year term for the Firepower 2110 IPS, Malware Defense and URL subscription |
|
L-FPR2110T-TMC-3Y |
3-year term for the Firepower 2110 IPS, Malware Defense and URL subscription |
|
L-FPR2110T-TMC-5Y |
5-year term for the Firepower 2110 IPS, Malware Defense and URL subscription |
|
FPR-MSP-SSD= |
Malware Storage Pack SSD for SSD slot 2 |
|
FPR2K-SLIDE-RAILS= |
Slide rail kit for 4-post EIA-310-D racks |
|
FPR2K-RM-BRKT= |
Spare rack-mount brackets |
|
FPR2K-CBL-MGMT= |
Cable management brackets |
|
FPR2K-SSD100= |
100 GB SSD spare for Firepower 2110 and 2120 |
|
Supported SFP for the fixed SFP ports | |
|
Supported SFP for the fixed SFP ports | |
|
Supported SFP for the fixed SFP ports | |
|
Supported SFP for the fixed SFP ports | |
|
Supported SFP for the fixed SFP ports |
Specifications
| Parameter | Specification | Parameter | Specification |
|---|---|---|---|
| Product ID | FPR2110-NGFW-K9 | Software application | Cisco Firepower Threat Defense |
| Integrated I/O | 12 x 10M/100M/1GBASE-T Ethernet interfaces (RJ-45), 4 x 1 Gigabit (SFP) Ethernet interfaces | Network modules | No network module bay |
| Maximum number of interfaces | Up to 16 total Ethernet ports | Integrated network management ports | 1 x 10M/100M/1GBASE-T Ethernet port (RJ-45) |
| Serial port | 1 x RJ-45 console | USB | 1 x USB 2.0 Type-A (500mA) |
| Throughput: FW + AVC (1024B) | 2.6 Gbps | Throughput: FW + AVC + IPS (1024B) | 2.6 Gbps |
| Throughput: IPS (1024B) | 2.6 Gbps | TLS | 365 Mbps |
| Maximum concurrent sessions, with AVC | 1 million | Maximum new connections per second, with AVC | 14K |
| IPSec VPN throughput (1024B TCP w/Fastpath) | 950 Mbps | Maximum VPN peers | 1,500 |
| AVC | Standard, more than 4,000 applications plus geolocations, users and websites; OpenAppID custom detectors | Cisco security intelligence | Standard, with IP, URL and DNS threat intelligence |
| Cisco Firepower NGIPS | Available with the IPS license | Cisco AMP for networks | Available with the Malware Defense license; Threat Grid sandboxing available |
| URL filtering | More than 80 categories, more than 280 million URLs categorized, with the URL Filtering license | High availability | Active/standby |
| Local management | Firepower Device Manager | Centralized management | Management Center or Cisco Defense Orchestrator |
| Licenses | Essentials included and required; IPS, Malware Defense, URL Filtering and Cisco Secure Client optional | DRAM | 16 GB |
| Cavium NPU RAM | 8 GB | Flash | 8 GB (nominal) |
| SSD storage | 1 x 100 GB SSD, 1 x spare slot (for MSP) | Power supply configuration | Single integrated 250W AC power supply, not field-replaceable |
| Redundancy | None | AC input voltage | 100 to 240V AC |
| AC maximum input current | < 2.7A at 100V | AC maximum output power | 250W |
| AC input frequency | 50 to 60 Hz | AC efficiency | >88% at 50% load |
| System power | 100/240V AC 1.9 A (at 100 VAC), 50 to 60 Hz | Fan modules | Integrated fans, not field-replaceable |
| Airflow | Front to rear, cold aisle to hot aisle (I/O side) | Noise | 56 dBA @ 25C; 74 dBA at highest system performance |
| Dimensions (H x W x D) | 1.73 x 16.90 x 19.76 in. (4.4 x 42.9 x 50.2 cm) | Form factor (rack units) | 1RU |
| Rack mountable | Fixed mount brackets included (2-post); mount rails optional (4-post EIA-310-D rack) | Weight | 7.3 kg (16.1 lb) with 2 SSDs |
| Temperature: operating | 0°C to 40°C (32°F to 104°F) | Temperature: nonoperating | -20°C to 65°C (-4°F to 149°F) |
| Humidity: operating | 10 to 85% noncondensing | Humidity: nonoperating | 5 to 95% noncondensing |
| Altitude: operating | 10,000 ft (max) | Altitude: nonoperating | 40,000 ft (max) |
| Regulatory compliance | CE markings per directives 2004/108/EC and 2006/108/EC | Safety certifications | UL 60950-1, CAN/CSA-C22.2 No. 60950-1, EN 60950-1, IEC 60950-1, AS/NZS 60950-1, GB4943 |
| EMC: emissions | 47CFR Part 15 Class A (FCC Class A), AS/NZS CISPR22 Class A, CISPR22 Class A, EN55022 Class A, ICES003 Class A, VCCI Class A, EN61000-3-2, EN61000-3-3, KN22 Class A, CNS13438 Class A, EN300386, TCVN7189 | EMC: immunity | EN55024, CISPR24, EN300386, KN24, TVCN 7317, EN-61000-4-2, EN-61000-4-3, EN-61000-4-4, EN-61000-4-5, EN-61000-4-6, EN-61000-4-8, EN61000-4-11 |
| Supported SFPs (fixed ports) | GLC-TE, GLC-SX-MMD, GLC-LH-SMD, GLC-EX-SMD, GLC-ZX-SMD; first supported in Threat Defense 6.2 / ASA 9.12 | Package contents | Chassis, RJ-45 to DB-9 console cable, one country-specific power cord, two rack-mount brackets, ground lug kit; SFPs and cable management brackets only when ordered |
| Supply chain assurance | Cisco Trust Anchor Technologies |
Get More Information
Need pricing, stock, or shipping details for the FPR2110-NGFW-K9 ? Layer23-Switch can help you check current availability, lead time, and delivery options for this. Send us the part number, quantity, and destination country via live chat or email [email protected] for a fast quotation.
Quality Certifications
Customer Reviews
Questions & Answers
-
Which spare PID replaces a failed FPR2110-NGFW-K9 chassis?
-
How much memory does FPR2110-NGFW-K9 have?
-
Which safety and EMC standards does FPR2110-NGFW-K9 meet?
-
What are the AC input and efficiency ratings of FPR2110-NGFW-K9?
Warranty
Layer23-Switch.com offers genuine, high-quality ICT products at competitive wholesale prices—ensuring exceptional value without compromising quality.
All items are brand new, original, and factory-sealed.
Upon request, each unit can be fully tested and verified by a Cisco CCIE-certified engineer to ensure perfect working condition before shipment.
Our Cisco CCIE-certified experts provide free professional support via phone, email, online chat, or remote login—helping you deploy and troubleshoot with confidence.
If you are not satisfied with your purchase, you may request an exchange or full refund. Our customer service team will guide you through the return process quickly and smoothly. Visit Return Policy page for more information.
We support multiple secure payment and logistics options, backed by industry-leading verification:
Visit How to Pay page for more information
Extended, Worry-Free Warranty Coverage Factory New Sealed Enterprise Hardware:
· 3 Years Factory New Sealed
Visit Warranty Policy page for more information
Verify, plan, and comparewith confidence
Use practical tools to check device details, review lifecyclemilestones, and compare hardware before you buy.
Standard Services
Personalized Service, Superior Product Maintenance for Ultimate Satisfaction.
- Projects and Technical Support
- Easy Purchasing Supply
- Product Lifecycle Protection
- Exclusive F3 Team Support
Customized Support for Your Needs with CCIE, HCIE, HPE ASE, etc.
No surprises, no disappointments. Just a clean transaction.
Installed during our maintenance window. Completed ahead of schedule. Wish the lead time was a bit shorter, but product quality made up for it.
Their professionalism is on par with the largest distributors. Shipping took a couple extra days, but product itself is perfect.
We need security for our community. This device provides it. Trustworthy seller.
This firewall… it’s a beauty. Locks everything down. Easy peasy lemon squeezy.