FPR3105-NGFW-K9 – 8x1G RJ45 + 8×1/10G SFP+ Ports – 1x 1/10G Network Module Slot – NGFW Firewall

Shop Expert-Recommended Accessories for the FPR3105-NGFW-K9
Explore optics, stacking accessories, modules, and power supplies—all verified by our engineers for use with this model.-

SFP-10G-SR-S
10GBASE-SR SFP+ - S-Class - 400m OM4 MMFOriginal price was: $853.95.$52.00Current price is: $52.00. -
SFP-10G-LR-S
10GBASE-LR SFP+ - S-Class - 10km SMFOriginal price was: $2,439.88.$150.00Current price is: $150.00. -
GLC-LH-SMD
1000BASE-LX/LH SFP - 10km SMF / 550m MMF - DOMOriginal price was: $1,260.58.$95.80Current price is: $95.80. -
GLC-TE
1000BASE-T SFP - RJ-45 Cat5 Copper - 100m ReachOriginal price was: $570.10.$70.00Current price is: $70.00. -
GLC-SX-MMD
1000BASE-SX SFP - MMF 850nm - DOMOriginal price was: $633.46.$59.00Current price is: $59.00.
Why Layer23-Switch
Stocked, Shipped and Supported by One Team
Ships in 1 Business Day
In-stock orders leave our Hong Kong or U.S. warehouse within 1 business day after payment, with tracking by email.
LSCare Warranty
3years on enterprise equipment
Free CCIE Support
Certified engineers help before and after you buy. Reply within 1 business day by email or live chat.
Verify Before You Pay
100%factory-sealed
Get label and serial photos before shipment, and check every serial number with Cisco.
FPR3105-NGFW-K9 Description
The FPR3105-NGFW-K9 is a Cisco Secure Firewall 3105 appliance that runs Threat Defense as a 1RU next-generation firewall at the internet edge. With firewall, application visibility and IPS enabled, the appliance is rated at 10 Gbps on 1024B packets and supports 1.5 million sessions and 2,000 VPN peers across 8 RJ-45 and 8 1/10G SFP+ ports. High availability on the FPR3105-NGFW-K9 comes from a two-unit pair, because the 3105 does not support clustering.
Quick Specs
|
Parameter |
Specification |
|---|---|
|
Software image |
Cisco Secure Firewall Threat Defense |
|
Form factor |
1RU |
|
Fixed data ports |
8 x 10M/100M/1GBASE-T RJ-45, 8 x 1/10G SFP+ |
|
Network module slot |
1 slot for 1/10G modules; up to 24 Ethernet ports in total |
|
Throughput: FW + AVC + IPS (1024B) |
10 Gbps |
|
TLS throughput |
3.2 Gbps |
|
IPsec VPN throughput (1024B TCP, fastpath) |
5.5 Gbps |
|
Maximum concurrent sessions, with AVC |
1.5 million |
|
Maximum new connections per second, with AVC |
90,000 |
|
Maximum VPN peers |
2,000 |
|
High availability |
Active/standby or active/active pair; clustering not supported |
|
Default power supply |
FPR3K-PWR-AC-400, 400W AC (one of two bays filled) |
|
Supported Threat Defense releases |
7.3 and later, except 7.4.0 |
Product Performance
Key Features
Application visibility for more than 4,000 applications and Security Intelligence feeds come standard with Threat Defense. IPS, Malware Defense and URL filtering are added through L-FPR3105T licenses, where T covers Security Intelligence and IPS, M or AMP covers malware defense, and C or URL covers URL filtering.
Firewall with application visibility, the full FW + AVC + IPS profile and dedicated NGIPS are all rated at 10 Gbps on 1024B packets. These are lab ratings; the enabled features, protocol mix, packet sizes and software release all move the result on a live link.
Decryption sets a much lower ceiling than inspection. TLS throughput is 3.2 Gbps with half the traffic as TLS 1.2 using AES256-SHA and 2048-bit RSA keys. A policy that decrypts most sessions should be sized from that figure, not from the 10 Gbps rating.
IPsec VPN throughput is 5.5 Gbps for 1024B TCP traffic over Fastpath, and the appliance terminates up to 2,000 VPN peers.
Two appliances can run as an active/standby or active/active high-availability pair. Clustering is not supported on the 3105, and a second unit adds failover rather than cluster capacity.
The single network module slot takes the 16 fixed ports to as many as 24. FPR3K-XNM-8X10G and the 1G and 10G hardware bypass modules are recognized; the 8-port 25G, 4-port 40G and 2-port 100G modules can be inserted but the software does not recognize them.
Application Scenarios
At the internet edge of a regional office, the firewall stands between the core switch and the service provider circuits and applies access control, IPS and URL filtering to traffic in both directions.
Remote workers using Cisco Secure Client connect to the appliance as their VPN headend, and branch offices bring their site-to-site IPsec tunnels to the same unit.
Between two data center segments, the appliance can run in dedicated IPS mode, where a hardware bypass network module keeps paired ports forwarding traffic if the appliance fails.
Product Comparison
|
Parameter |
FPR3105-NGFW-K9 | |||
|---|---|---|---|---|
|
Software image |
Threat Defense |
ASA |
Threat Defense |
Threat Defense |
|
Stateful inspection firewall throughput (1500B UDP) |
Not applicable |
10.0 Gbps |
Not applicable |
Not applicable |
|
Throughput: FW + AVC + IPS (1024B) |
10 Gbps |
Not applicable |
17.0 Gbps |
21.0 Gbps |
|
IPsec VPN throughput |
5.5 Gbps (1024B TCP, Fastpath) |
5.5 Gbps (450B UDP L2L) |
8 Gbps (1024B TCP, Fastpath) |
10 Gbps (1024B TCP, Fastpath) |
|
Maximum concurrent sessions |
1.5 million with AVC |
1.5 million firewall connections |
2 million with AVC |
4 million with AVC |
|
Maximum VPN peers |
2,000 |
2,000 |
3,000 |
7,000 |
|
Integrated I/O |
8 x RJ-45 and 8 x 1/10G SFP |
8 x RJ-45 and 8 x 1/10G SFP |
8 x RJ-45 and 8 x 1/10G SFP |
8 x RJ-45 and 8 x 1/10G SFP |
|
Network modules |
8 x 1/10G Options |
8 x 1/10G Options |
8 x 1/10G Options |
8 x 1/10G Options |
|
Power supply configuration |
Single 400W AC; dual AC or DC optional |
Single 400W AC; dual AC or DC optional |
Single 400W AC; dual AC or DC optional |
Single 400W AC; dual AC or DC optional |
FPR3105-NGFW-K9 runs Threat Defense on the same 3105 hardware as FPR3105-ASA-K9, which runs ASA and is rated 10.0 Gbps for 1500B UDP stateful inspection rather than 10 Gbps with AVC and IPS on 1024B packets. Sites standardized on ASA order FPR3105-ASA-K9. Inspected traffic above 10 Gbps, more than 1.5 million sessions or more than 2,000 VPN peers moves the site to FPR3110-NGFW-K9, rated 17.0 Gbps with 2 million sessions and 3,000 peers. FPR3120-NGFW-K9 goes further, to 21.0 Gbps, 4 million sessions and 7,000 peers, with 10 Gbps of IPsec VPN against 5.5 Gbps. All four share the same I/O, 1/10G module options and single 400W AC supply.
Ordering Checklist
- Threat Defense subscription: Order an L-FPR3105T term PID such as L-FPR3105T-TMC-3Y; T, TC, TM, TMC, URL and AMP each come as -1Y, -3Y or -5Y. Malware and URL features need the Threat (T) license, so URL-only or AMP-only lines leave them unusable.
- Smart Licensing account: Set up the end customer’s Smart Licensing account in Smart Software Manager before the Threat Defense order. Every ordered license is deposited into that account.
- Network module: Choose FPR3K-XNM-8X10G, FPR3K-XNM-6X1SXF, FPR3K-XNM-6X10SRF, FPR3K-XNM-6X10LRF or FPR3K-XNM-8X1GF. The 8-port 25G, 4-port 40G and 2-port 100G modules can be installed but are not recognized by the software.
- Second power supply: Add FPR3K-PWR-AC-400= for 1+1 redundancy, since the appliance ships with one 400W AC supply. DC sites order FPR3K-PWR-DC-400= units instead, because AC and DC supplies cannot share a chassis.
- Second SSD: Add FPR3K-SSD900= for SSD slot 2, which is reserved for software RAID1. An SSD from another firewall platform, such as the 2100 Series, cannot be used.
- Rack kit: Add FPR3K-SLIDE-RAILS= for a 4-post rack or FPR3K-BRKT= for 2-post mounting; Cisco recommends the slide rails. Rails and brackets are in the package only if ordered.
Optional Add-ons
|
Model |
Description |
|---|---|
|
400W AC power supply for the empty bay, giving 1+1 redundancy | |
|
400W DC power supply for DC sites; replaces AC supplies rather than mixing with them | |
|
900 GB NVMe SSD for slot 2 software RAID1 | |
|
FPR3K-XNM-8X10G= |
8-port 1/10G SFP+ network module |
|
FPR3K-XNM-6X10SRF= |
6-port 10G SR multimode hardware bypass network module |
|
FPR3K-XNM-6X10LRF= |
6-port 10G LR single-mode hardware bypass network module |
|
FPR3K-XNM-6X1SXF= |
6-port 1G SX multimode hardware bypass network module |
|
FPR3K-XNM-8X1GF= |
8-port 10/100/1000Base-T hardware bypass network module |
|
10G SFP+ optic supported on the 3105 fixed SFP+, management and FPR3K-XNM-8X10G ports | |
|
10G SFP+ optic supported on the 3105 fixed SFP+, management and FPR3K-XNM-8X10G ports | |
|
1G copper SFP supported on the 3105 fixed SFP+, management and FPR3K-XNM-8X10G ports | |
|
FPR3K-FAN= |
Spare dual fan module |
|
FPR3K-SLIDE-RAILS= |
Slide rail kit for 4-post racks |
|
FPR3K-BRKT= |
Rack-mount brackets for 2-post mounting |
|
FPR3K-CBL-MGMT= |
Cable management brackets |
|
FPR3K-FIPS-KIT= |
FIPS opacity shield kit |
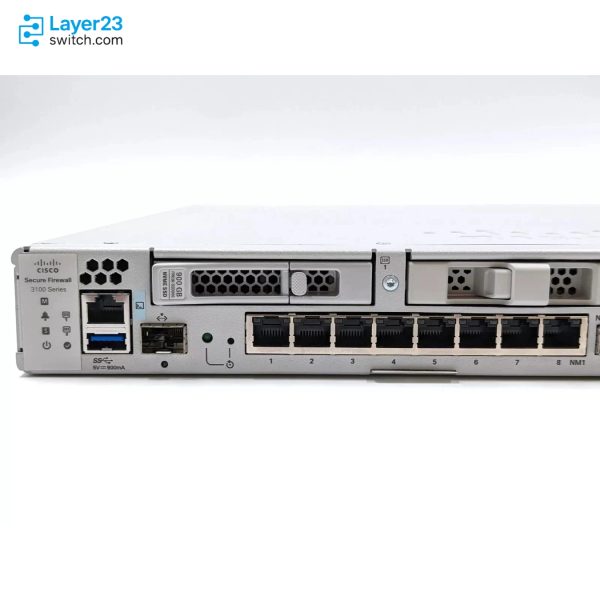
Front View
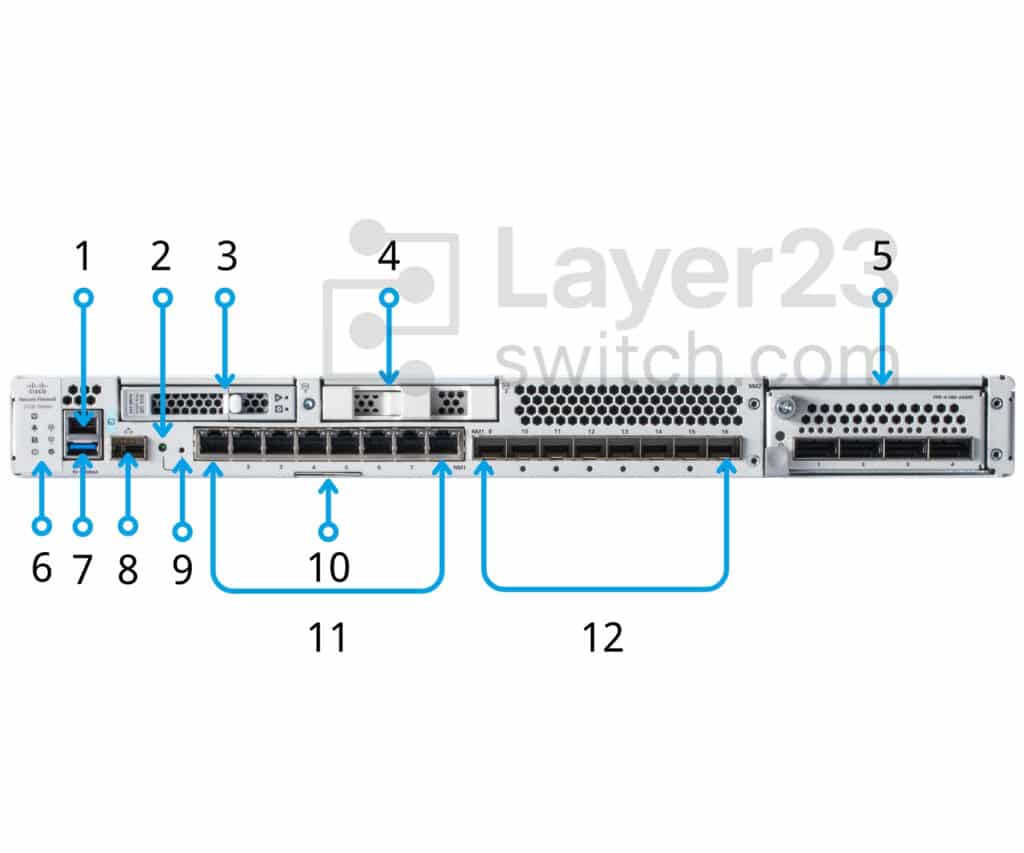
|
1 |
RJ-45 console port |
2 |
Recessed factory reset button |
|
3 |
SSD-1 |
4 |
SSD-2 |
|
5 |
Network module (NM-2) |
6 |
System LEDs |
|
7 |
Type A USB 3.1 port |
8 |
Gigabit Ethernet management port:Secure Firewall Threat Defense—Management 0 (also referred to as Management 1/1 and Diagnostic 1/1)ASA—Management 1/1 |
|
9 |
Reset button LED |
10 |
Pullout asset card with chassis serial number, getting started guide QR code, and LTP QR code |
|
11 |
Eight fixed RJ-45 ports (NM-1)RJ-45 ports named Ethernet 1/1 through 1/8 left to right; for a list of supported SFPs. |
12 |
Eight fixed SFP+ ports (NM-1)SFP+ ports named Ethernet 1/9 through 1/16 left to right; for a list of supported SFPs. |
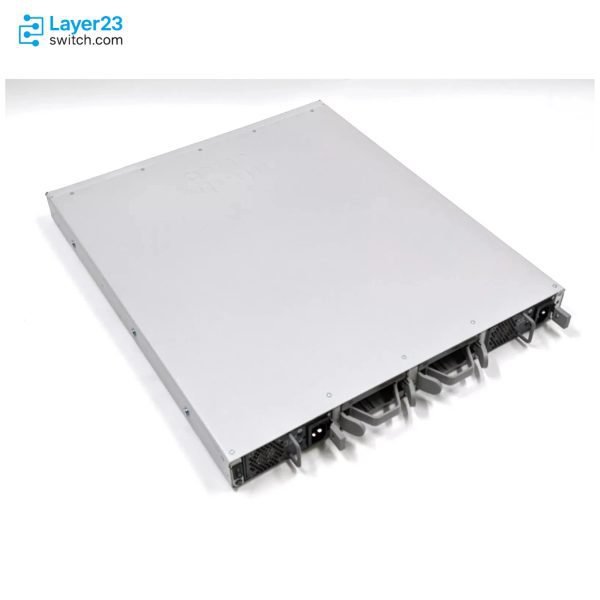
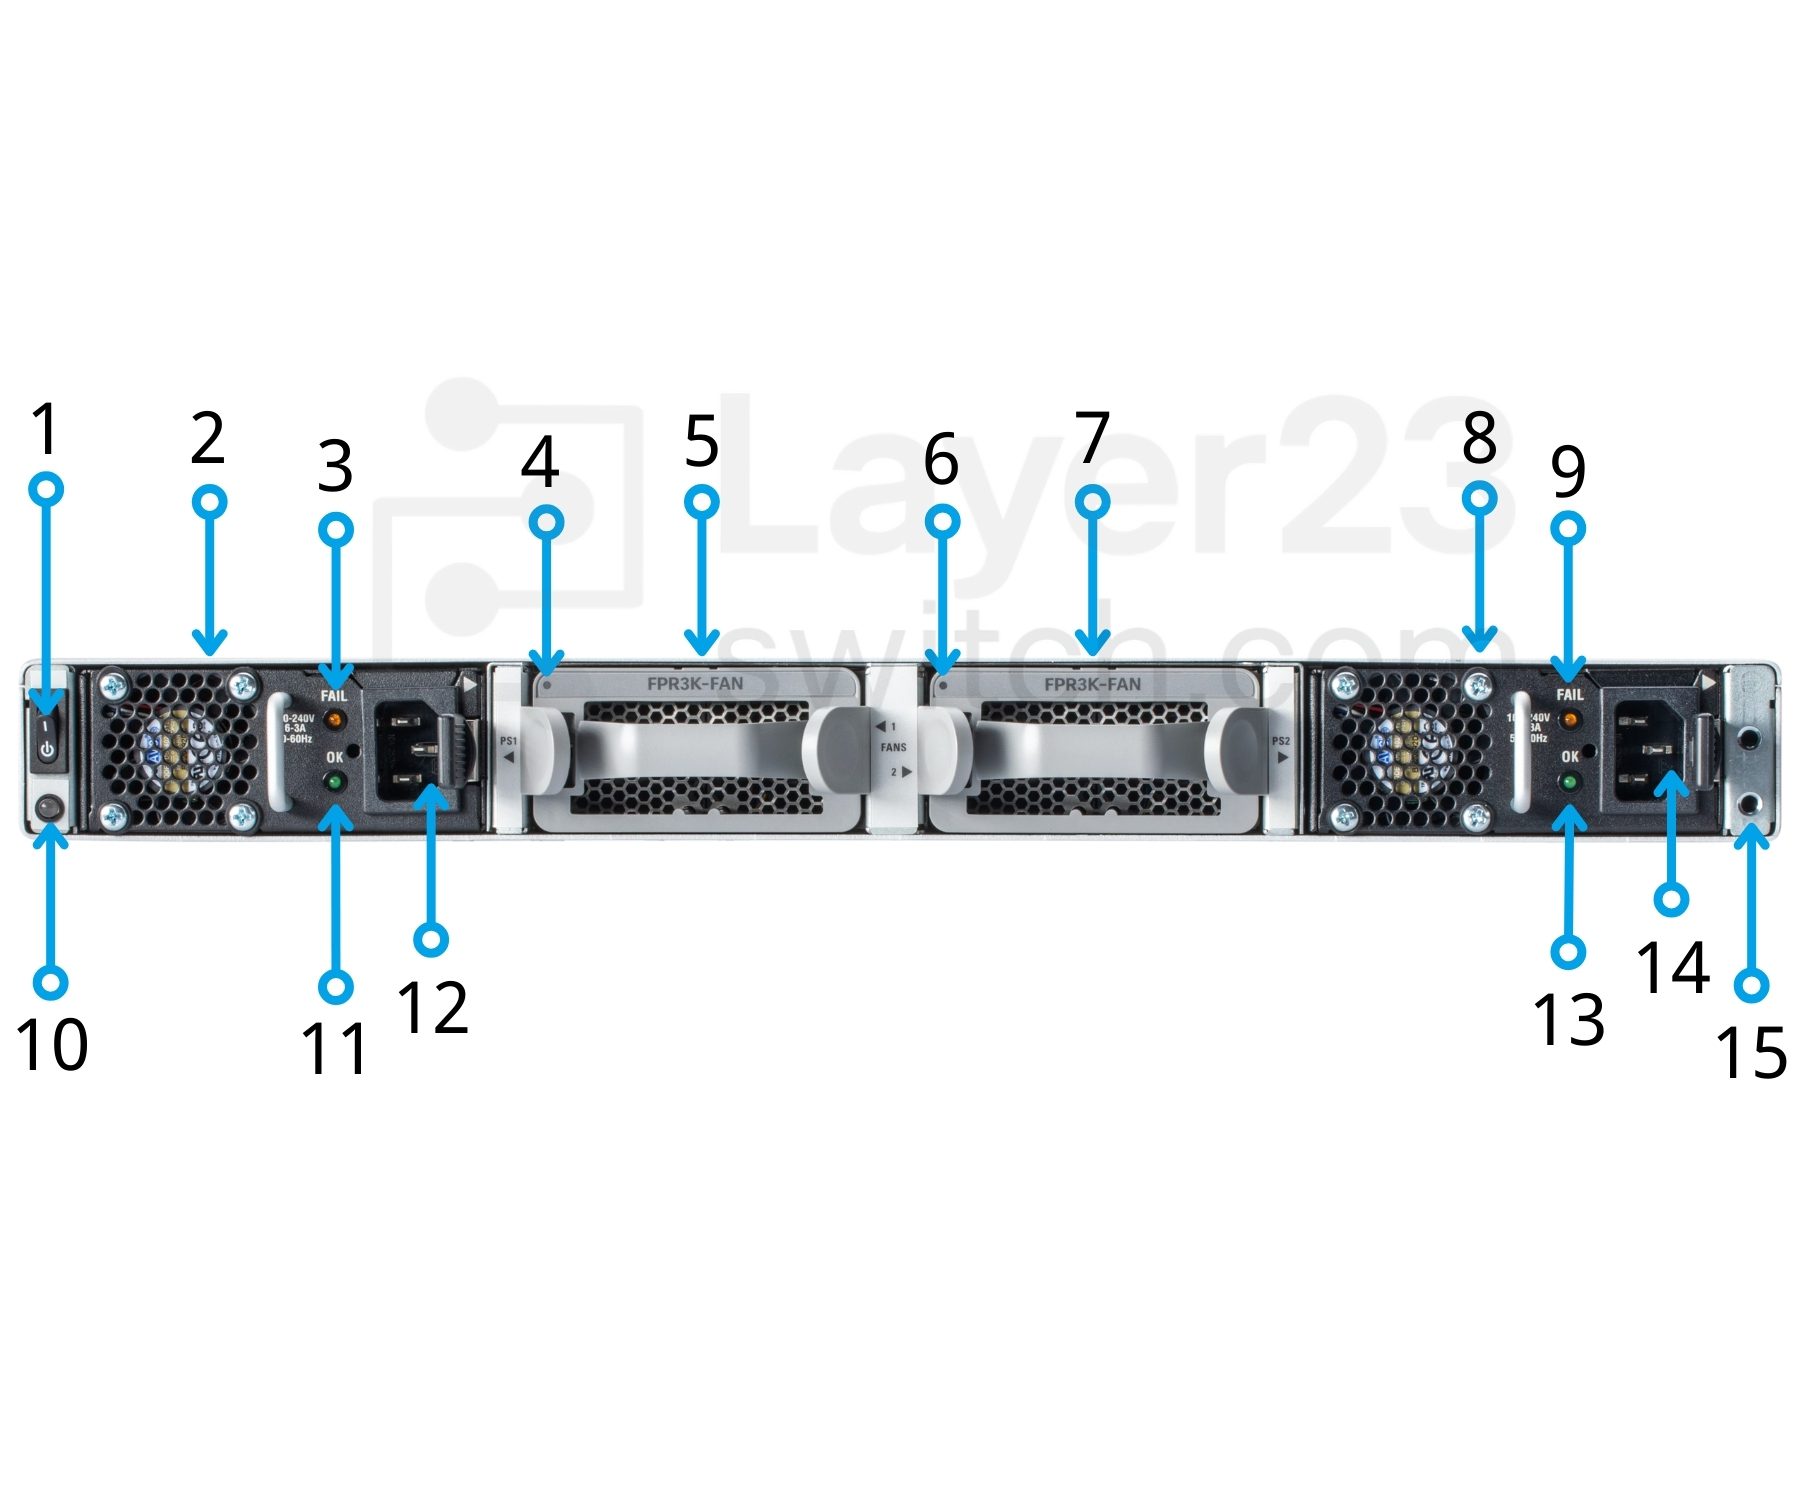
Rear View
|
1 |
Power on/off switch |
2 |
Power supply module (PSU-1) |
|
3 |
Power supply module FAIL LED (PSU-1) |
4 |
Fan module LED (FAN-1) |
|
5 |
Fan module (FAN-1) |
6 |
Fan module LED (FAN-2) |
|
7 |
Fan module (FAN-2) |
8 |
Power supply module (PSU-2) |
|
9 |
Power supply module FAIL LED (PSU-2) |
10 |
Chassis power LEDNote This power LED has the same behavior as the front panel LED. See Front Panel LEDs for more information. |
|
11 |
Power supply module OK LED (PSU-1) |
12 |
Power supply module connector (PSU-1) |
|
13 |
Power supply module OK LED (PSU-2) |
14 |
Power supply module connector (PSU-2) |
|
15 |
Two-post grounding padNote The two-post grounding lug and two screws are included in the accessory kit. |
— |
Specifications
| Parameter | Specification | Parameter | Specification |
|---|---|---|---|
| Product ID | FPR3105-NGFW-K9 | Cisco ordering description | Cisco Secure Firewall 3105 Appliance with Threat Defense software |
| Software image | Cisco Secure Firewall Threat Defense | Supported Threat Defense releases | 7.3, 7.4.1–7.4.x, 7.6, 7.7 and 10.x (7.1, 7.2 and 7.4.0 not supported) |
| Local on-device management | Firewall Device Manager, included with the Threat Defense image | Centralized management | Firewall Management Center or Cisco Security Cloud Control |
| Form factor (rack units) | 1RU | Integrated I/O | 8 x 10M/100M/1GBASE-T Ethernet interfaces (RJ-45), 8 x 1/10 Gigabit (SFP) Ethernet interfaces |
| Network module slots | 1 | Network modules | 8 x 1/10G options: FPR3K-XNM-8X10G, FPR3K-XNM-6X1SXF, FPR3K-XNM-6X10SRF, FPR3K-XNM-6X10LRF, FPR3K-XNM-8X1GF |
| Maximum number of interfaces | Up to 24 total Ethernet ports | Integrated network management ports | 1 x 1/10G SFP |
| Serial port | 1 x RJ-45 console | USB | 1 x USB Type-A (900 mA) |
| SSD storage | 1x 900 GB NVMe SSD, 1x spare slot for software RAID1 | DRAM | 64 GB |
| Throughput: FW + AVC (1024B) | 10 Gbps | Throughput: FW + AVC + IPS (1024B) | 10 Gbps |
| Throughput: NGIPS (1024B) | 10.0 Gbps | Maximum concurrent sessions, with AVC | 1.5 million |
| Maximum new connections per second, with AVC | 90,000 | TLS throughput | 3.2 Gbps (50% TLS 1.2 traffic, AES256-SHA, RSA 2048B keys) |
| IPSec VPN throughput (1024B TCP w/Fastpath) | 5.5 Gbps | Maximum VPN peers | 2,000 |
| High availability | Active/active, active/standby | Clustering | Not supported on the 3105 |
| Application visibility (AVC) | Standard, more than 4000 applications, geolocations, users, and websites | Cisco security intelligence | Standard, with IP, URL, and DNS threat intelligence |
| Cisco Secure IPS, malware Defense, Secure malware analytics | Available as subscriptions | URL filtering | More than 80 categories, more than 280 million URLs categorized |
| Deployment modes | Firewall or dedicated IPS | Q-in-Q (stacked VLAN) | Up to two 802.1Q headers per packet on inline sets and passive interfaces |
| Cisco trust anchor technologies | Included | Power supply configuration | Single 400W AC; dual 400W AC optional; single or dual 400W DC optional |
| Default power supply | FPR3K-PWR-AC-400, 400W AC (one installed) | AC input voltage | 100 to 240V AC |
| AC maximum input current | < 6A at 100V | AC maximum output power | 400W |
| AC input frequency | 50 to 60 Hz | DC input voltage | -48V to -60VDC |
| DC maximum output power | 400W | DC efficiency | >88% at 50% load |
| Power redundancy | 1+1 AC or DC with dual supplies; AC and DC supplies cannot be mixed | Fan modules | 2 hot-swappable fan modules (2 fans each), 3+1 redundancy |
| Airflow | Front to rear (I/O side to non-I/O side), cold aisle to hot aisle | Noise | 65 dBA at 25°C, 74 dBA maximum |
| Sound power | 72 dB typical, 80 dB maximum | Dimensions (H x W x D) | 1.75 x 17 x 20 in. (4.4 x 43.3 x 50.8 cm) |
| Weight | 10.5 kg (23 lb) with 1 power supply, 1 network module, fan modules, 1 SSD | Mounting | 19-inch rack; optional 2-post brackets or 4-post EIA-310-D slide rails |
| Temperature: operating | 0°C to 40°C (32°F to 104°F) | Temperature: nonoperating | -20°C to 65°C (-4°F to 149°F) |
| Altitude: operating | 10,000 ft (max) | Altitude: nonoperating | 40,000 ft (max) |
| Safety certifications | UL 62368-1, CAN/CSA-C22.2 No. 62368-1, EN 62368-1, IEC 62368-1, IEC 60950-1, AS/NZS 62368-1, GB4943 | EMC: emissions | FCC 47CFR15 Class A, AS/NZS CISPR 32 Class A, EN55032/CISPR 32 Class A, ICES-003 Class A, VCCI Class A, KS C 9832 Class A, CNS-13438 Class A, EN61000-3-2, EN61000-3-3 |
| EMC: immunity | IEC/EN61000-4-2, IEC/EN61000-4-3, IEC/EN61000-4-4, IEC/EN61000-4-5, IEC/EN61000-4-6, IEC/EN61000-4-11, KS C 9835 | EMC: ETSI/EN | EN 300 386, EN55032/CISPR 35, EN55024/CISPR 24, EN55035/CISPR 35, EN61000-6-1 |
| Regulatory compliance | CE markings |
Quality Certifications
Customer Reviews
Questions & Answers
-
What throughput does FPR3105-NGFW-K9 reach with firewall, AVC and IPS enabled?
-
Do IPS, Malware Defense and URL filtering on FPR3105-NGFW-K9 need a subscription?
-
Which legacy network module PIDs does FPR3105-NGFW-K9 not recognize?
-
How many SSD, power supply and fan module bays does FPR3105-NGFW-K9 have, and how many are populated?
-
Which Threat Defense releases can run on FPR3105-NGFW-K9?
-
What is the weight of FPR3105-NGFW-K9 with its standard components?
Warranty
Layer23-Switch.com offers genuine, high-quality ICT products at competitive wholesale prices—ensuring exceptional value without compromising quality.
All items are brand new, original, and factory-sealed.
Upon request, each unit can be fully tested and verified by a Cisco CCIE-certified engineer to ensure perfect working condition before shipment.
Our Cisco CCIE-certified experts provide free professional support via phone, email, online chat, or remote login—helping you deploy and troubleshoot with confidence.
If you are not satisfied with your purchase, you may request an exchange or full refund. Our customer service team will guide you through the return process quickly and smoothly. Visit Return Policy page for more information.
We support multiple secure payment and logistics options, backed by industry-leading verification:
Visit How to Pay page for more information
Extended, Worry-Free Warranty Coverage Factory New Sealed Enterprise Hardware:
· 3 Years Factory New Sealed
Visit Warranty Policy page for more information
Verify, plan, and comparewith confidence
Use practical tools to check device details, review lifecyclemilestones, and compare hardware before you buy.

Layer23 is exactly the kind of vendor we look for.
We’ve made Layer23 part of our standard procurement process.
I opened it next to a unit we bought direct. Same box, same wrapping, same product.
Lead times are long elsewhere, but Layer23 delivered in a week.
Design improvements are noticeable. FPGA acceleration is real. Fast delivery.